Overview
Synadia Protect (protect) is a NATS protocol proxy that sits in front of NATS
clusters. It is a WAF (Web Application Firewall) for NATS. It inspects,
evaluates, and enforces security policies on connections and message protocols
flowing through it. The goal of Protect is to manage security at the edge — not
application-level concerns like data format validation. The docs assume
familiarity with NATS concepts: pub/sub, subjects and authentication.
What it does
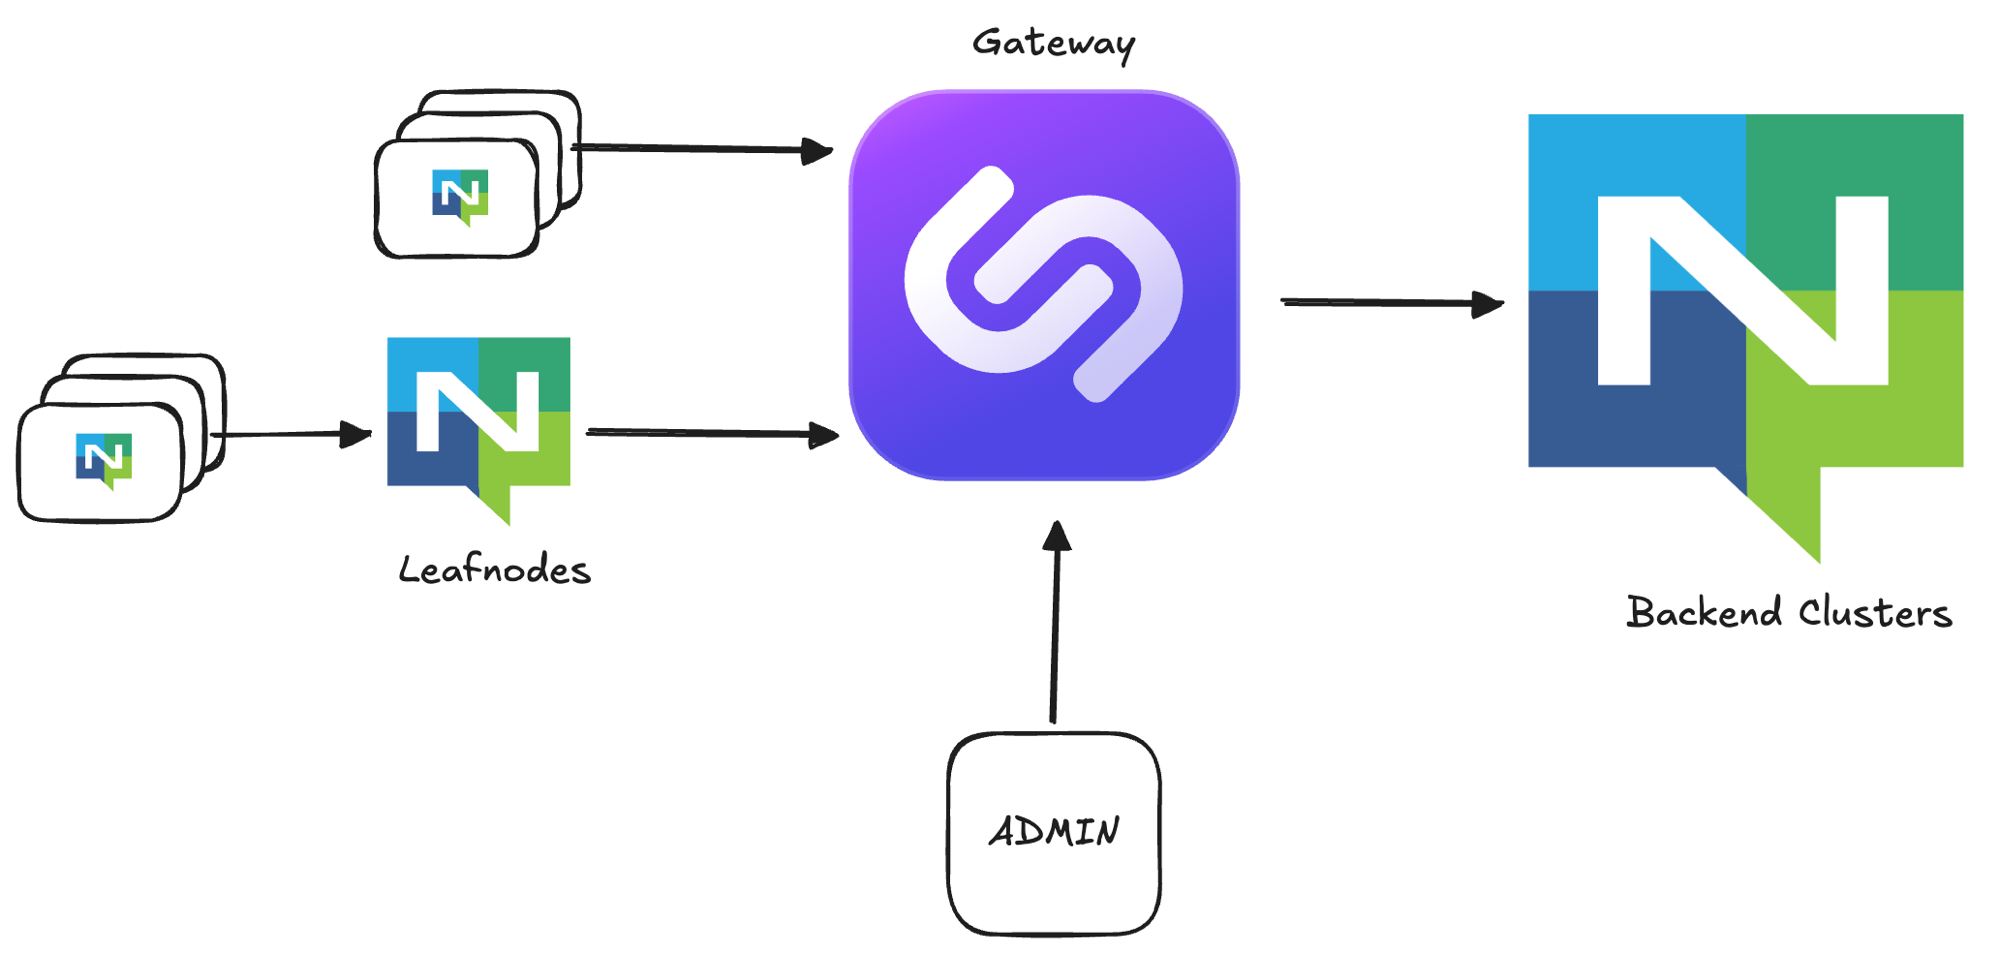
- Proxies NATS client and leafnode traffic to backend servers and/or clusters
- Evaluates rules against connections and messages in real time — by subject, header, payload, source IP, time of day, and more before being forwarded to the backend.
- Allows, denies, or suspends traffic based on the outcome of a policy
- Captures client traffic into traces for forensic analysis — tracing can be activated by a policy or on-demand
- Produces audit logs for every non-
allowpolicy decision, suitable for SIEM integration
How it works
The gateway's unit of configuration is a port. Each port is an independent
proxy — it evaluates protocol traffic against a set of rules (a ruleset), and
forwards allowed traffic to a backend NATS cluster.
Rules are packaged into bundles — versioned, signed collections that can be
installed, tested, and activated on a port without restarting the gateway.
The gateway ships with built-in rules covering common use cases (CIDR filtering, header inspection, payload matching, time-based access). Custom rules can be written using the Expr language.
Deployment modes
Standalone
A single gateway managing its own policies.
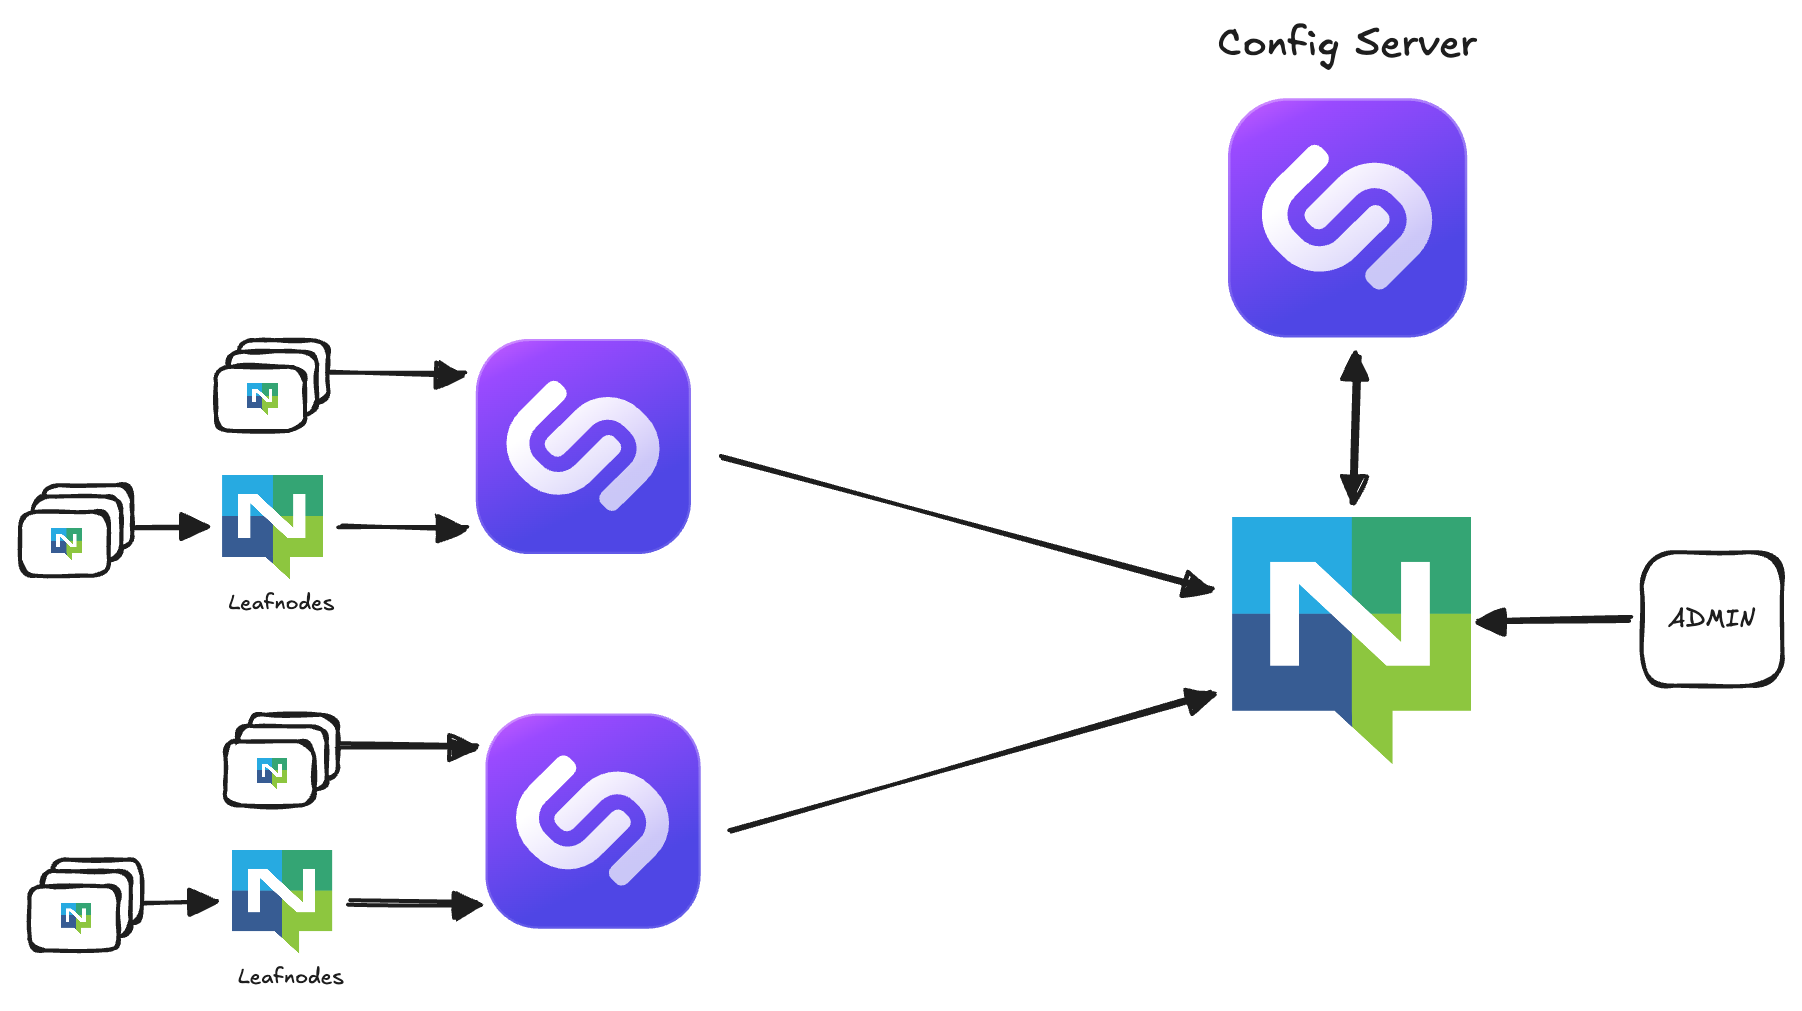
Configuration server + managed gateways
Centralized management for a fleet of gateways.